
Is BCM Dead? Why Business Continuity Needs a Resilience Reframe
What happens when the plan depends on everyone else?
Most organisations have invested heavily in business continuity: plans, crisis teams, cyber response arrangements, supplier assessments and incident playbooks. Many of those plans may be perfectly sound, but what happens when their success depends on a supplier, utility, technology provider or public service that cannot respond as expected, or which chooses to prioritise somebody else?
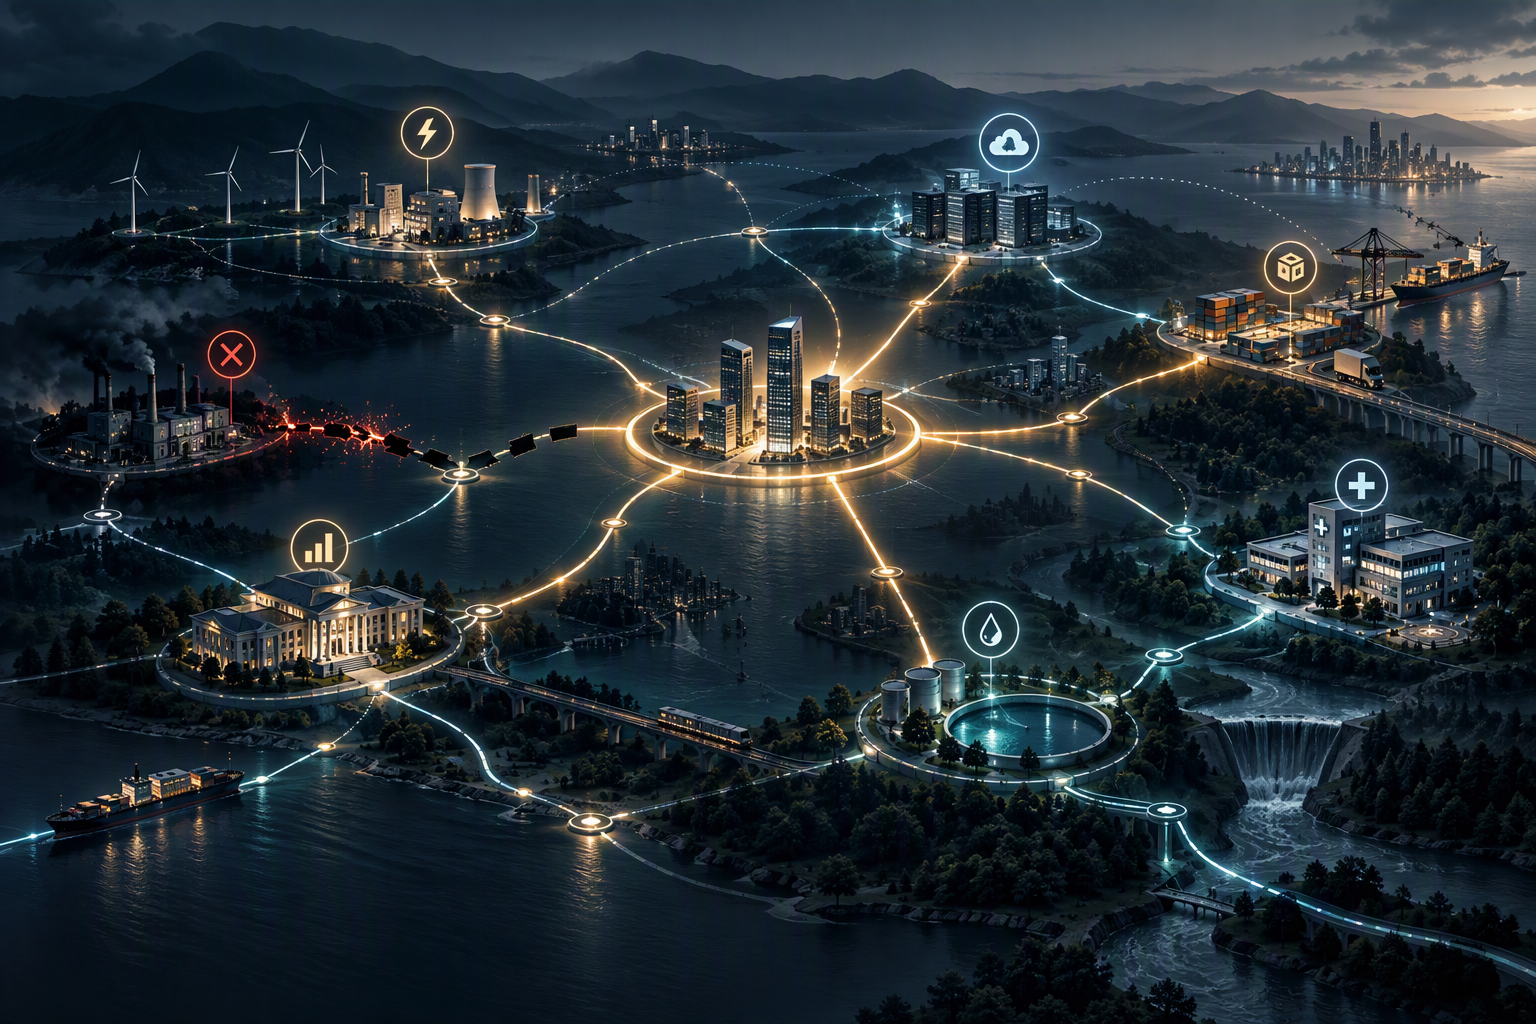
Organisations are now more interconnected, more dependent on third parties and infrastructure, and more exposed to disruption that moves across organisational and sector boundaries. So the question is no longer simply whether our own recovery plans work, it’s whether the wider system they depend on will work with us.
That takes us into a different set of questions: what absolutely must continue, what does it depend on, where are the critical handoffs, and who decides when priorities collide? It also changes how we should test resilience. Instead of simply validating the plan, we need to test the assumptions underneath it, including through wargaming and decision rehearsal when normal operating conditions no longer apply.
Start with what must continue
In our recent article on resilience Resilience starts with essential outcomes – Brave Consultancy, we argued for starting with the outcomes an organisation must continue to deliver when normal conditions no longer apply. That remains the right starting point. But this article takes the next step: what happens when delivering those outcomes depends on other organisations?
Traditional risk management often starts with “what could go wrong?” Business continuity tends to ask how a process or service would be restored. Both matter, but resilience needs to connect those questions back to what the organisation is trying to sustain and the wider system it relies upon.
That creates a golden thread from objectives and essential outcomes through the dependencies, vulnerabilities, controls and capabilities that determine whether they can continue to be delivered. It also raises a practical question about the organisation’s minimum viable operating state. What absolutely has to keep working? What could reduce, stop or be deferred? How much degradation is tolerable, and for how long?
These are not simply operational questions. They involve choices and trade-offs, and some ultimately belong in the boardroom.
Resilience does not stop at the organisational boundary
Every organisation makes assumptions about the system around it. Suppliers will deliver. Communications and cloud services will remain available. Energy will be restored. Key third parties will prioritise us. Government or regulators will provide direction.
Some of those assumptions may be reasonable, but an assumption is not the same as a resilience capability. The challenge is not simply to identify critical suppliers or systems. It is to understand how dependencies interact and what happens when several organisations experience pressure at the same time.
Increasingly, some of our most important vulnerabilities therefore sit not within organisations, but at the interfaces between them.
A wider shift is already happening
NATO’s revised 2026 Seven Baseline Requirements for Resilience provide an interesting signal of this wider shift.
They are primarily concerned with national and collective resilience rather than corporate regulation, but NATO now explicitly describes resilience as a whole-of-society challenge involving the private sector, with a strong focus on critical services, strategic dependencies, cascading effects and sustained disruption. The requirements also encourage civil and commercial organisations to consider crisis and conflict contingencies within their continuity planning.
The point for business is not that organisations should start planning like governments or defence ministries. It is that the assumptions on which resilience depends are being tested by a more interconnected, contested and potentially prolonged operating environment.
That was also reinforced at the recent NATO CIMIC Foresight Conference, where a recurring theme was that practical weaknesses often emerge where organisations and institutions meet: in handoffs, ownership, information flows and coordination.
And that matters well beyond defence or critical national infrastructure.
The vulnerability may be in the handoff
Think about the handoffs inside a large organisation: risk into executive management, cyber into crisis management, suppliers into procurement, business units into the corporate centre. Then extend that across organisational boundaries.
A signal may exist but fail to reach the person able to act. The organisation with the information may not have the authority to decide. Several parties may assume somebody else owns the issue. Each component can therefore function reasonably well while the wider system still fails.
We have spent years strengthening individual nodes. The harder resilience question may now be whether the links between them work under pressure.
What happens when priorities differ?
Interdependence becomes harder still when everyone can act, but their priorities do not align.
Imagine one scarce generator during a prolonged power disruption. A hospital needs it for patient safety. A water facility needs it for public health. A data centre needs it to maintain essential digital services. The organisation controlling it may need the same resource to remain viable.
Who takes priority?
Without clear mechanisms, choices may be made by default; through contractual rights, existing relationships, liability or simply whoever can escalate most effectively. The same issue can arise within organisations and between business and society. What is essential to the organisation may not be what government or wider society needs it to prioritise during severe disruption.
The resilience question is whether those tensions have been considered before the pressure arrives. Who decides? What information do they need? What thresholds would change priorities?
This is why resilience increasingly looks like a decision discipline, not simply a planning discipline.
Wargaming: from testing the plan to rehearsing the decision
This is where wargaming can add considerably more value than a conventional continuity exercise.
There is nothing wrong with testing whether procedures work and people know their roles. But successfully following a plan tells us relatively little about what happens when its assumptions fail.
A good wargame introduces pressure, ambiguity, scarcity and competing priorities. It forces leaders to decide what to protect, what to sacrifice and when to change course, and then confront the consequences. It can also test something conventional exercises often miss: the interfaces between plans and organisations.
What happens if two critical dependencies fail together? If a supplier prioritises somebody else? If disruption lasts weeks rather than hours? If the information needed to decide is incomplete? Done well, wargaming moves resilience from plan testing to decision rehearsal. The aim is not simply to prove the plan works, but to discover where it doesn’t while there is still time to do something about it.
From resilience activity to resilience confidence
Boards often receive resilience information through separate lenses: risk, BCM, cyber, procurement, strategy and assurance. Each may be accurate, yet directors can still be left to join the dots themselves.
The goal should be a connected view of what needs to be sustained, what it depends on, where vulnerabilities and thresholds sit, and how confident management is that the organisation can respond when circumstances change. Technology can help make those connections visible, but fundamentally this remains a governance and human challenge.
Frameworks create clarity. Technology provides better intelligence. People still make the decisions.
So what should organisations do differently?
A practical starting point is to take one essential outcome and follow a critical dependency beyond the organisational boundary.
What are you assuming the other party will do during prolonged disruption? Who else will be competing for its capacity? What happens if its priorities differ from yours? Who would know, and who would decide?
Then put those assumptions into an exercise.
More broadly, boards and executive teams should understand what must continue, identify the dependencies behind it, define acceptable degradation and minimum operating states, use wargaming to rehearse difficult decisions, and connect resilience more directly into governance and assurance.
None of this means abandoning risk management, business continuity, crisis management or cyber resilience. It means connecting them around the organisation’s ability to continue delivering what matters.
Is BCM dead?
No.
But BCM on its own is increasingly unlikely to be enough.
A business continuity plan can describe how an organisation intends to respond to disruption. What it cannot tell you is how another organisation will behave under the same pressure, whose needs it will prioritise, or what happens when the assumptions between plans collide.
Resilience asks the broader question: can we continue to deliver what matters when circumstances change, assumptions fail and difficult choices have to be made?
Strategy determines what matters. Risk provides the intelligence. Resilience determines the response.
Increasingly, the organisations that will prove most resilient will be those that understand not only how their own system works, but what happens when it meets everybody else’s.
AUTHOR.
EMMA PRICE.